
- Winnti APT41 Targets Japanese Firms in RevivalStone Cyber Espionage Campaign
- Who is Winnti APT41?
- <strong>Understanding the RevivalStone Campaign</strong>
- Winnti’s Advanced Malware Arsenal
- Evolution of Winnti Malware
- <strong>The Broader Cybersecurity Landscape</strong>
- <strong>Defensive Strategies Against APT Attacks</strong>
- <strong>Conclusion</strong>
Winnti APT41 Targets Japanese Firms in RevivalStone Cyber Espionage Campaign
Cyber espionage has been a growing concern, with state-backed hacking groups launching sophisticated attacks to gain strategic advantages. One such actor, Winnti APT41, has resurfaced with a new cyber campaign, RevivalStone, targeting Japanese manufacturing, materials, and energy sectors. This article delves into the tactics, techniques, and implications of this cyber threat while offering insights into how organizations can defend themselves against such attacks.
Who is Winnti APT41?
Winnti, a China-linked Advanced Persistent Threat (APT) group, has been active since at least 2012, conducting cyber espionage operations worldwide. Notorious for its dual-purpose activities—state-sponsored espionage and financially motivated attacks—APT41 has repeatedly exploited vulnerabilities in critical infrastructure.
Understanding the RevivalStone Campaign
Attack Overview
RevivalStone, as reported by Japanese cybersecurity firm LAC, aligns with a subset of APT41, also tracked as:
- Earth Freybug (Trend Micro)
- Operation CuckooBees (Cybereason)
- Blackfly (Symantec)
This campaign targeted public-facing enterprise applications and leveraged sophisticated malware to establish persistent remote access while evading security measures.
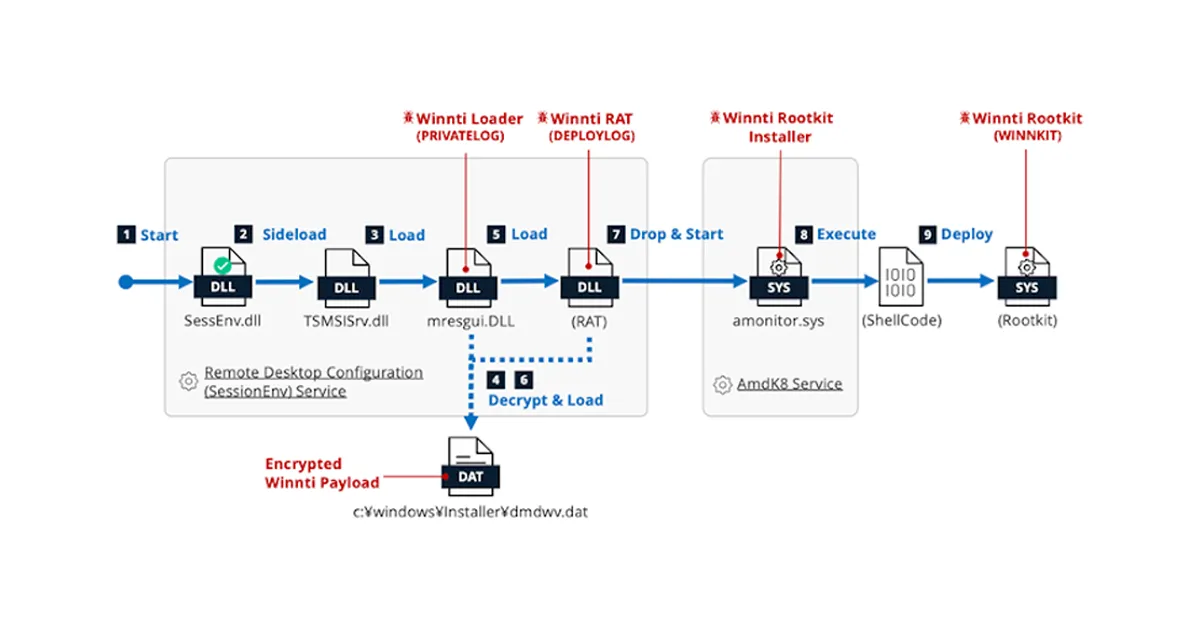
Key Attack Techniques
- SQL Injection Exploitation
- Attackers leveraged an SQL injection vulnerability in an unspecified Enterprise Resource Planning (ERP) system.
- This allowed them to drop web shells such as China Chopper and Behinder to infiltrate the system.
- Credential Harvesting & Lateral Movement
- After gaining access, the group collected user credentials to move laterally within the organization.
- Managed Service Providers (MSPs) were also compromised to expand the reach of the malware.
- Malware Deployment
- The attackers deployed an enhanced version of the Winnti malware, indicating ongoing evolution and improvement of their toolset.
- The malware suite included obfuscation techniques, updated encryption, and evasion features that make detection and mitigation challenging.
- Supply Chain Attack Vector
- The attackers leveraged third-party service providers to infiltrate multiple organizations simultaneously.
- This attack method increased the scope of damage while reducing the chance of immediate detection.
Winnti’s Advanced Malware Arsenal
Notable Malware Variants Used in RevivalStone
- DEATHLOTUS – A CGI-based passive backdoor supporting file creation and execution.
- UNAPIMON – A defense evasion tool written in C++.
- PRIVATELOG – A loader that drops Winnti RAT (DEPLOYLOG) and a kernel-level rootkit known as WINNKIT.
- CUNNINGPIGEON – Uses Microsoft Graph API for stealthy command execution.
- WINDJAMMER – A rootkit for network interception and covert communication.
- SHADOWGAZE – A passive backdoor exploiting IIS web server ports.
Evolution of Winnti Malware
The newly identified Winnti malware (possibly v5.0) incorporates:
- Advanced obfuscation techniques
- Updated encryption algorithms
- Better evasion capabilities against security products
- Enhanced persistence mechanisms to survive system reboots
The Broader Cybersecurity Landscape
Other Threat Actors and Recent Trends
In parallel, another China-backed group, Daggerfly (Bronze Highland/Evasive Panda), was found deploying SSHDInjector, a Linux-based malware suite for SSH hijacking and data exfiltration.
These ongoing campaigns emphasize the increasing sophistication of cyber threats from state-sponsored actors, requiring businesses to strengthen their cybersecurity posture proactively.
Recent High-Profile Incidents
- 2023 Attack on Southeast Asian Enterprises – APT41 was linked to several data breaches in financial and government institutions.
- Supply Chain Attack on Tech Firms – Using compromised MSPs, Winnti managed to infiltrate multiple technology companies in 2024.
- Critical Infrastructure Targeting – Attacks on energy and materials sectors align with geopolitical interests, potentially compromising national security.
Defensive Strategies Against APT Attacks
-
Implement Robust Access Controls
- Use multi-factor authentication (MFA) to secure critical accounts.
- Restrict privileged access using zero-trust principles.
-
Regular Vulnerability Assessments & Patch Management
- Periodically scan systems for SQL injection vulnerabilities.
- Keep ERP systems and other enterprise applications up to date.
-
Advanced Threat Detection & Response
- Deploy Endpoint Detection and Response (EDR) tools to detect unusual activity.
- Monitor network traffic for signs of covert communication.
- Use deception technology to lure attackers into controlled environments for analysis.
-
Employee Awareness & Training
- Conduct regular phishing simulations and cybersecurity training.
- Educate staff on common attack vectors like social engineering.
- Implement incident response drills to prepare teams for real-world cyber threats.
-
Incident Response & Threat Intelligence Sharing
- Establish a rapid incident response plan.
- Collaborate with cyber threat intelligence (CTI) communities to stay informed on evolving threats.
- Utilize threat-hunting techniques to identify hidden adversaries within networks.
Conclusion
The RevivalStone cyber espionage campaign by Winnti APT41 underscores the persistent threats faced by global industries, particularly those aligned with China’s strategic interests. Organizations must adopt proactive defense measures to counter these evolving cyber threats.
By leveraging advanced security tools, employee awareness programs, and real-time threat intelligence, businesses can mitigate risks and strengthen their cybersecurity resilience against sophisticated APT attacks.
Stay ahead of cyber threats! Subscribe to our threat intelligence reports and ensure your organization is protected against evolving cybersecurity risks.
Frequently asked questions.
Answers connected directly to this article and its subject.
01 What is APT41, and why is it significant?
APT41 is a China-linked cyber espionage group known for conducting both state-sponsored espionage and financial cybercrime.
02 What industries are most at risk from APT41 attacks?
Sectors such as manufacturing, materials, energy, and technology are prime targets due to their strategic importance.
03 How does Winnti malware evade detection?
Winnti malware uses rootkits, obfuscation techniques, and encrypted communications to avoid detection by security software.
04 How can organizations protect themselves from SQL injection attacks?
Companies should regularly patch software, conduct security audits, and use web application firewalls (WAFs) to prevent SQL injection exploits.



